Crypto Hacks Hit $1.18 Billion in Q3 2026, Worst Quarter Since Early 2025, Hacken Reports
Published October 15, 2026, 11:15 UTC. Based on Hacken's Q3 2026 security report and reporting by CoinTelegraph, PANews, cryptobreaking.com and bitnewsbot.
Crypto hackers stole $1.18 billion across 107 incidents in the third quarter of 2026, according to a quarterly security report from Hacken published October 15, 2026, making it the most damaging quarter for crypto theft since Q1 2025. Roughly $906 million of the losses, about 77%, traced back to compromised suppliers or developer tools, publicly disclosed fixes that had never been deployed, or infrastructure sitting outside the scope of security audits, Hacken said.
The four incidents that ate 80% of the quarter
Losses were heavily concentrated. Just four incidents accounted for roughly 80% of the quarter's stolen value, according to Hacken's figures, which were reported by CoinTelegraph. Bitget lost $387 million in a September hot-wallet attack. The Liquid Network exploit drained $320 million. Tectonic, a lending protocol, lost $120 million. A Coldcard firmware vulnerability was tied to about $115 million in losses. The other 98 incidents each caused less than $10 million in damage, with a median loss of $670,000.
The side door: 77% came through suppliers and tools
The report's headline finding is where the money went missing. About 77% of Q3's losses did not come from zero-day smart contract bugs at the core of protocols, but from the periphery: compromised third-party suppliers, developer tools, known fixes that had been published but never applied, and infrastructure that sat outside any security review, according to Hacken. Smart contract exploits were still the most common attack vector by count, with 71 incidents causing $228 million in losses, but the big money left through the supply chain. Hacken urged the industry to harden third-party suppliers, developer tooling and other external infrastructure, and recommended expanding audits to cover oracles, bridges, custody systems, signing authorities and other privileged components.
The $387 million that came back: white hats, rollbacks and freezes
About a third of the stolen funds were recovered. Hacken said roughly $387 million, about 33% of gross losses, was returned or reversed after the attacks, according to CoinTelegraph. After the Liquid Network hack, self-described white hats returned $272 million, about 85% of what was taken. In the Tectonic case, Cronos validators rolled back 114 minutes of settled blockchain history, reversing about $111.2 million of $120.4 million in affected borrowing. Stablecoin issuers Circle and Tether froze about $340,000 linked to the Bitget theft. Operators covered another $410 million in user losses from their own reserves: Bitget's user protection fund covered $387 million, while Triple-A, Coinsbuy and TAC repaid about $22 million, making users whole even though the stolen assets stayed with the attackers. About $384 million, or 32% of gross losses, was neither returned nor covered.
Worst quarter since Q1 2025
The last time a quarter looked this bad was Q1 2025, when Bybit lost $1.4 billion to North Korean attackers, pushing that quarter's total to $1.6 billion, according to Hacken's comparison. The Q3 numbers line up with independent counts: Finbold Research calculated more than $1.17 billion stolen in Q3 2026 using SlowMist incident data, with September alone accounting for $762 million. CertiK put the figure at $1.26 billion across 247 incidents, according to CoinTelegraph. The spread reflects different counting methods, but the direction is the same: after $955 million lost in the entire first half of the year, per Finbold, the third quarter alone topped it.
This article is news reporting and is not investment advice.
Sources
- Hacken Q3 2026 security report, published October 15, 2026, primary source for the $1.18 billion total, 107 incidents, 77% supplier-tool attribution, the four largest incidents, recovery figures and audit recommendations
- CoinTelegraph, October 15, 2026, secondary coverage of Hacken's report, including the Liquid white-hat return, the Cronos rollback, the Circle and Tether freezes and operator compensation
- PANews, October 15, 2026, secondary summary of Hacken's Q3 findings: 107 incidents, $906 million supplier-tool attribution, median $670,000 loss and smart contract attack counts
- Finbold Research via SlowMist data, October 2026, independent Q3 count of more than $1.17 billion stolen, with September alone at $762 million and H1 2026 at $955 million
- CertiK via CoinTelegraph, October 2026, independent Q3 count of $1.26 billion across 247 incidents
MABOnChain Daily Brief
The key crypto and markets stories in one short, plain-language email. Free. Unsubscribe any time.
Prefer chat? Join us on Telegram Watch on YouTube
Keep reading
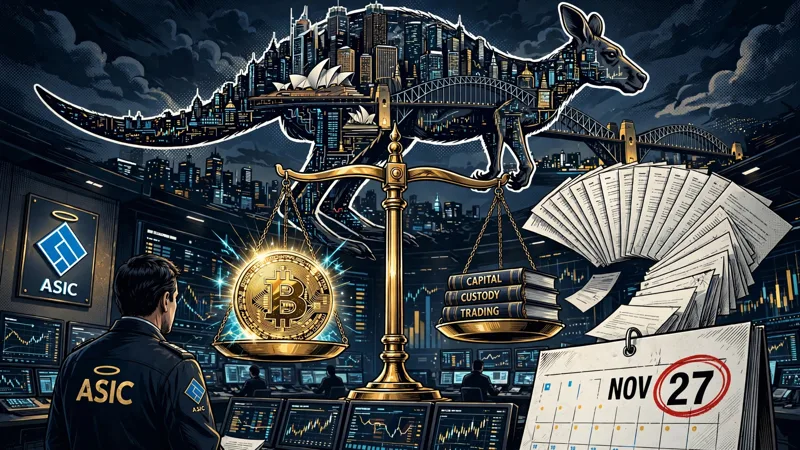
ASIC Opens Consultation on Capital, Custody and Trading Rules for Crypto Platforms, Targets April 2027 Rollout
Australia's financial watchdog ASIC opened a public consultation on October 15, 2026 on proposed capital, custody and trading standards for crypto platforms and digital asset custodians. Industry feedback is due November 27, final guidance is expected in March 2027, and the new licensing framework takes effect April 8, 2027.
StandX Shuts Down Perpetuals Exchange, Cancels Token Launch, and Airdrops DUSD to 237,000 Users
Decentralized perpetual futures exchange StandX said on October 15, 2026 it will wind down its trading and stablecoin operations, cancel its planned native token launch, and distribute a one-time DUSD stablecoin airdrop to its community of more than 237,000 users, following a strategic review of the business. Perpetual contracts go reduce-only on October 20, and DUSD redemption and withdrawals end January 31, 2027.
South Korea Plans Cybersecurity Overhaul for Finance Firms After Hacks Hit 16 Companies
South Korea's Financial Services Commission will tighten cybersecurity rules for financial institutions after an investigation into hacking incidents at 16 companies, including crypto exchanges Gopax and Prabang, exposed about 100,000 customer records. Larger firms would undergo vulnerability assessments at least twice a year, with stronger executive accountability and off-schedule inspections when urgent threats emerge.